Identify the problem before resetting anything
Forgetting a password is frustrating, but not every failed BDG Win login means that the password has been forgotten. An incorrect identifier, the wrong login tab, an unfamiliar destination, a restricted account, and an incomplete page can all produce a failed access attempt. Start by recording what the page actually says. A recovery process should respond to a credential problem that you have identified, rather than become the first experiment for every possible error.
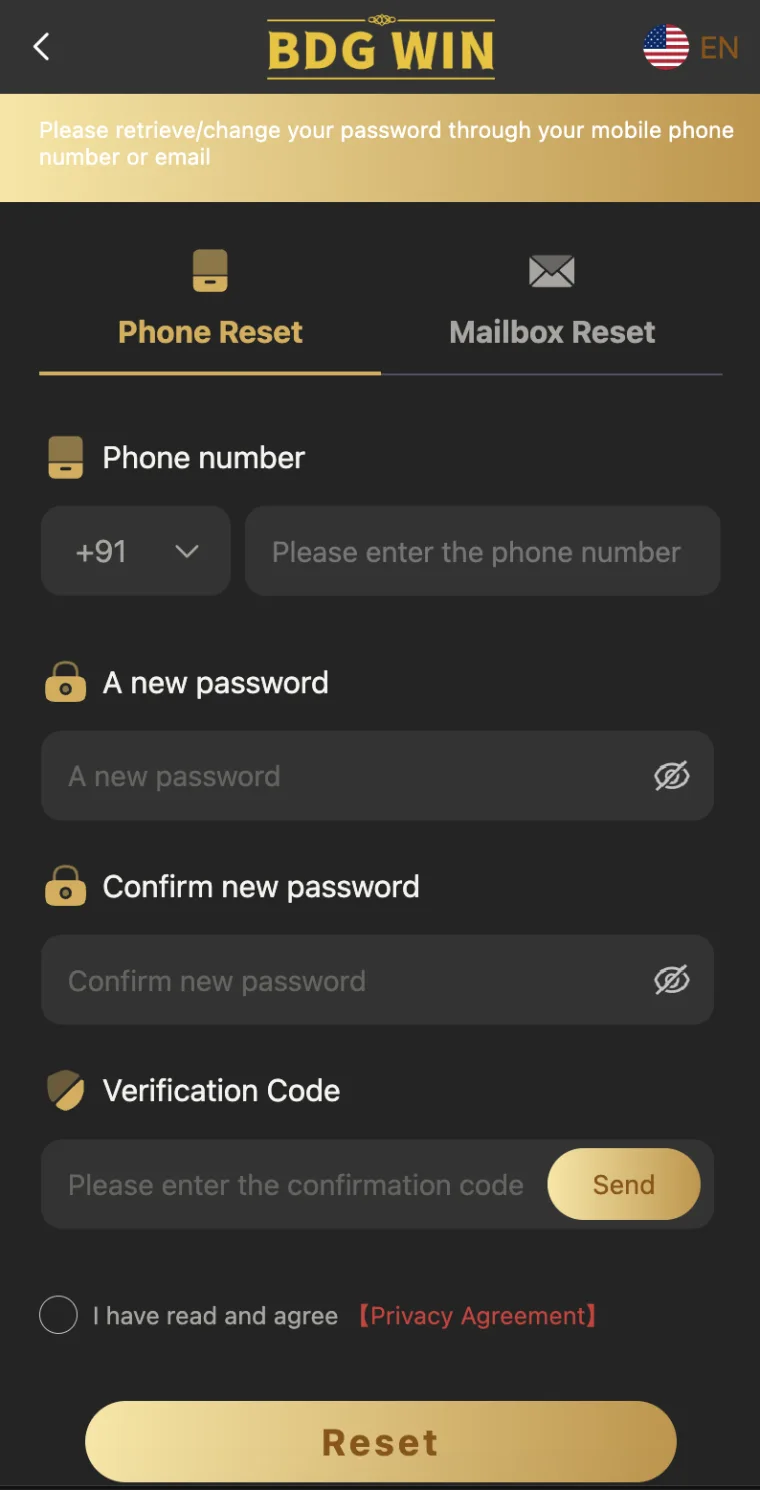
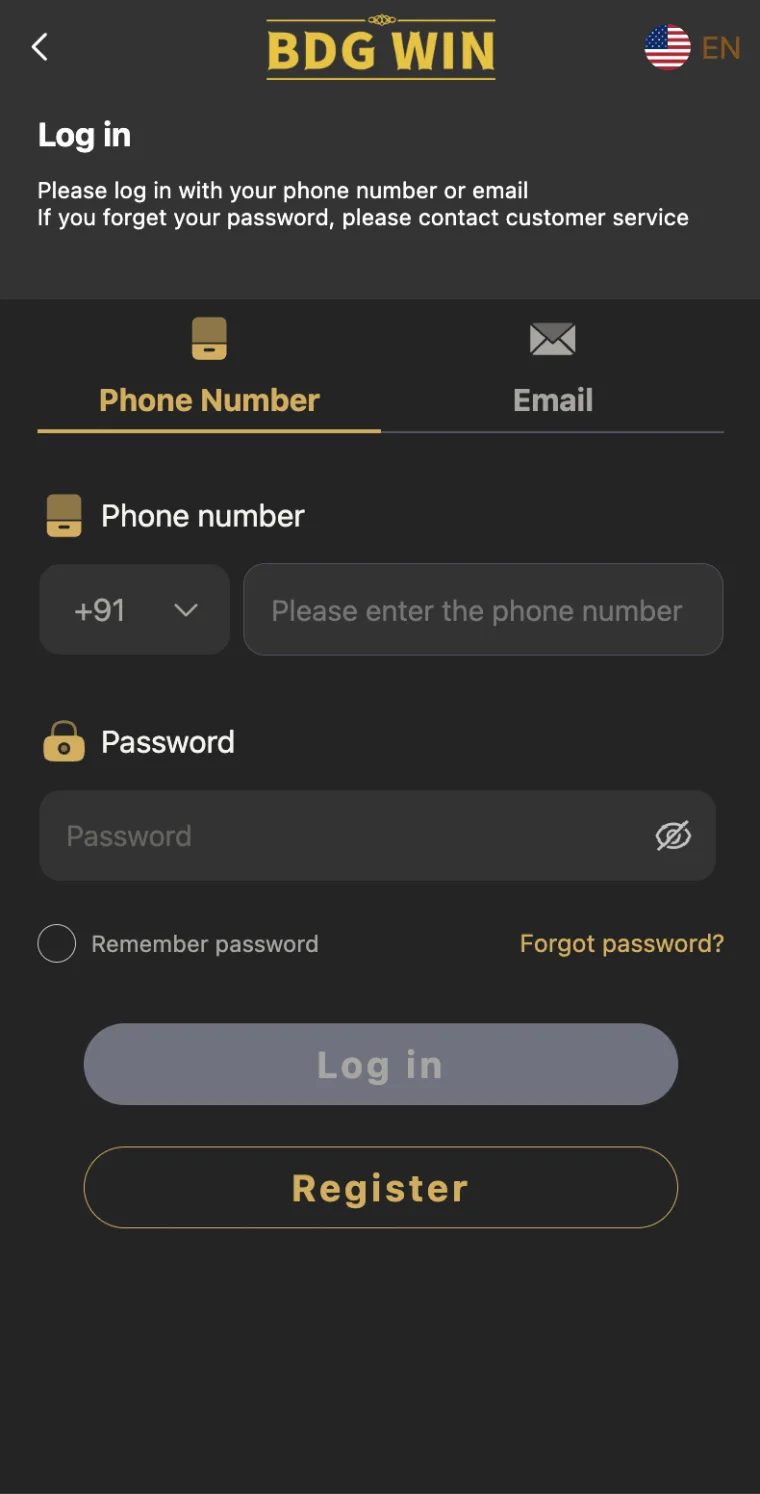
The supplied login reference includes a Forgot Password control. That is the only provider-specific recovery feature established by the material available for this guide. The live origin could not be verified during research, and the reference does not show the pages reached after selecting that control. This article therefore does not claim that recovery uses SMS, email, documents, support approval, a particular time limit, or a fixed sequence. It explains how to approach whichever legitimate recovery process the identified operator currently provides, with clear boundaries around what remains unknown.
Distinguish forgotten from possibly exposed
There are two very different reasons to replace a credential. You may no longer remember it, or you may believe someone else has learned it. The second situation deserves a broader review because simply remembering the old password would not resolve the concern. Write down why you are initiating recovery: an ordinary memory lapse, a failed saved credential, an unexpected change, or an interaction with a suspicious page.
If you submitted the same password to another site and now doubt that site, consider where else that credential was reused. General security guidance from Google recommends a unique password for each important account. This principle does not tell us anything about BDG Win's internal protections, but it explains why a reused credential creates a wider problem than one inaccessible account. Prioritize access to your email and other critical accounts through their own legitimate recovery routes. Do not use a suspected compromised page as the place to investigate unrelated credentials, and do not send a list of passwords to someone offering to audit them.
Confirm the account identifier privately
Before selecting a recovery control, establish which identifier you are trying to recover. Review the original registration record, an account reference you saved, or legitimate correspondence that you can evaluate carefully. The supplied login reference has phone and email tabs, but it does not prove that every account has both identifiers. Recovery instructions for the wrong identifier can send you down an unrelated path.
A phone number you currently own may differ from the number used at registration. An email that receives promotions may differ from an account login address. Keep these possibilities separate. Prepare a private note with the account information you can support and the information you are uncertain about. Do not post all of your possible numbers and addresses in a public help group. If you cannot identify the account, ask the verified operator what information is appropriate for locating it. An orderly account history helps a legitimate process; a pile of guessed identifiers usually makes the issue less clear.
Reach recovery from a destination you have evaluated
Navigate to the login interface through a route you have independently checked. Then inspect the final address before selecting Forgot Password or entering an identifier. An unexpected recovery message is not a reason to trust a link inside that message. A copied brand name, a convincing page color, and an urgent subject line do not establish who controls the destination.
The affiliate registration link supplied for this project is not a verified recovery route. This guide should not invent a reset URL by modifying that link, and readers should not treat arbitrary recovery links in search results as equivalent to the operator's own process. If you cannot verify the platform identity, pause the recovery attempt and investigate that first. Recovery can involve personal information and the power to change account access, so uncertainty about the recipient is material. A clear destination is part of the task, not an optional detail to check after a password has already been submitted.
Inspect the first recovery page without assuming the next
If the current Forgot Password control opens a recovery page, read the entire visible request before proceeding. Note the identifier it asks for, any explanation of the action, and any displayed support alternative. Do not infer the rest of the process from another service you have used. An email account provider, a banking application, and a gaming account may use entirely different ownership checks.
If the page asks for information that seems unrelated to account identification, stop and clarify why it is needed. This is especially important when the request moves to a separate chat or asks you to download software. A genuine task can become unsafe if it changes channels without an explanation. Preserve a redacted image of the request and the host for your own records. You do not need to complete an unfamiliar step merely to discover what comes after it. Understanding the purpose and recipient of each request is a reasonable condition for continuing through a recovery flow.
Understand what a recovery code authorizes
A code, if the current process uses one, is a credential for a particular action. The screenshot does not establish that BDG Win sends codes, so any discussion here is conditional. If you initiate a recovery request and receive a code, compare the message context with the action on the page. Do not read it aloud to a person who calls or messages you claiming to help.
A common social problem is treating the code as harmless because it is not the account's usual password. Its temporary nature does not make it appropriate to share. It may permit someone to complete a recovery action during the period in which it is valid. If a purported support contact asks for the code, stop and verify the interaction through a separate trusted route. Record that a code was requested or delivered, but omit the value from screenshots and support notes. The useful evidence is the timing, the destination, and the visible outcome, rather than the secret that could authorize access.
Avoid creating a confusing sequence of requests
If the recovery page allows another request after a delay, follow its current instructions rather than repeatedly pressing the control. Several overlapping requests can make it difficult to understand which message relates to which attempt. The guide cannot state how long any code remains valid or whether a newer request invalidates an older one; those are operator-specific details that have not been verified.
Keep a simple timeline: the moment you initiated the request, whether a response appeared, and whether a message arrived through the expected channel. If nothing arrives, inspect the identifier you supplied and the availability of the channel you control. Do not switch to a stranger's inbox or temporary number just to receive something. If delivery remains unresolved, ask the operator about the current process and provide the timeline without including any active secrets. A single well documented attempt gives support something coherent to evaluate. A stream of guesses and repeated requests often produces more uncertainty than it resolves.
When your old phone number is unavailable
Losing access to a registration number changes the recovery problem. You are no longer only replacing a password; you may also need to establish ownership without the usual contact method. The supplied materials do not establish whether the operator permits a number change, what proof it accepts, or whether recovery is possible in that situation. Avoid guides that promise a guaranteed solution without citing a current, specific process.
Prepare an account history using information you already possess, such as the registration period, any nonsecret account reference, and the last time you successfully used the account. Ask a verified support channel what evidence is required before sending documents. Do not contact the current holder of an old number and ask them to pass along codes, and do not use someone else's identity as a workaround. If the operator cannot provide an intelligible ownership process, preserve your records and stop rather than paying an unofficial intermediary who claims special access. An access problem does not justify creating a second ownership problem.
When your email address is inaccessible
If the legitimate recovery process depends on an email account you cannot access, first evaluate the email provider's own recovery process through its official support route. Keep the two accounts conceptually separate. Regaining an email account may restore a communication channel, but it does not by itself change the gaming account password or prove that the account accepts email login.
Avoid forwarding all mailbox contents to a helper or granting remote access simply because a single recovery message is missing. Your mailbox may contain unrelated personal and financial information. A focused recovery task should not require exposing that wider record to an affiliate publisher. If the account operator offers an alternative process, examine its stated requirements independently. Record which channel is unavailable and which channel remains under your control, then ask how the operator handles that combination. Do not assume that an address used for marketing messages can substitute for the original recovery address. The association must be established by the current account process.
Choose the replacement credential as a new decision
When a legitimate process reaches the point of setting a new password, choose a credential that is unique to this account and store it through a method you trust. Do not make a predictable variation of an old password merely to remember it more easily. Read the current form's requirements and distinguish them from generic password advice. A rule stated for a Google account is not automatically a rule for this service.
Consider the practical cause of the original failure. If you lost the password because it existed only in memory, creating another memory-only credential repeats the same problem. If multiple saved entries caused confusion, plan which entry will represent the new credential and how the obsolete one will be marked. If someone else may have learned the old value, consider other accounts where it was reused and review them through their own legitimate interfaces. A reset is most useful when it corrects the recordkeeping or exposure issue that led to it, rather than merely producing a different string of characters.
Store the new value before closing the confirmation
A recovery process can appear successful while the user's private records still contain the old credential. Before leaving the confirmation stage, make sure your password storage method contains the intended new value for the correct destination and account identifier. If a password manager asks whether to update an entry, review the account label privately so that you do not overwrite a different account by mistake.
Avoid saving the credential in a filename, a screenshot, a browser tab title, or an email to yourself. These methods can spread it into places that were never intended for secrets. If you keep an offline record, choose a private location appropriate to the sensitivity of the information. Do not include the actual password in a support ticket merely to show that a change occurred. A note saying password replaced on this date is enough for an access timeline. The goal is to make the next legitimate login straightforward without increasing the number of people or systems that can read the credential.
Establish success from the interface and a controlled check
A password change is not confirmed merely because a form stops spinning. Look for an explicit result in the current interface, and preserve any nonsecret confirmation reference. If the process instructs you to return to login, follow that route deliberately and use the new credential once. Avoid opening many competing tabs that leave you unsure which one reflects the current state.
If the new credential fails, record the exact response and identify whether the issue is the password, identifier, destination, or an additional account condition. Do not immediately reset again without understanding the result of the first attempt. A recovery loop can obscure an underlying mismatch in the identifier or a restriction that changing the password will not fix. Ask a focused support question with the sequence you observed. This guide cannot promise that replacing a password restores every type of account access. It addresses one credential question, while the operator's actual account status and eligibility rules remain separate matters.
Review other sessions only where the service actually supports it
Some services offer controls for reviewing active sessions or signing out other devices. The supplied reference does not establish that BDG Win provides these controls. If the current account interface does offer them, read the descriptions and use them with a clear understanding of which sessions will be affected. Do not assume that changing the password automatically ends every existing session.
If the reset followed a suspected exposure, ask the verified operator what effect the change has on other access. Keep the question specific: does this action invalidate existing sessions, and is there a documented way to review account activity? Avoid following an unofficial script that claims to perform hidden account security functions. A real control should have an identifiable place in the current service or a documented support process. If no control is available, record that limitation as part of your decision about future use. The absence of a visible option is not evidence that the option exists somewhere else and only requires a special payment or intermediary.
Recognize recovery offers that change the task
An unsolicited recovery offer often sounds attractive because it promises an immediate end to frustration. Examine what the person is actually asking you to do. A request for payment to reveal a password, remote control of your device, a code from your phone, or identity documents sent through a private account changes the interaction from explanation to sensitive access delegation.
An affiliate relationship does not establish authority to reset platform accounts. A social profile displaying the brand name does not establish that it represents the operator. Ask for a verifiable support channel and return to that channel independently rather than relying on the person's own link. If you already shared a secret with a suspicious contact, stop the conversation and review the affected accounts through legitimate routes. Keep evidence of the interaction without distributing the secret further. The objective is to contain exposure and restore clarity, not to prove trust by sharing additional information. Pressure, secrecy, and a demand to act immediately are reasons to slow the process down.
Build an evidence packet for a difficult recovery case
A recovery support packet should explain the problem without trying to answer identity questions the operator has not asked. Begin with a short chronology: account created approximately then, last successful access then, current identifier under control or unavailable, recovery attempted at this time, and this exact result displayed. Include the final host and the device context where relevant.
Provide a redacted screenshot of the error if it adds something the text cannot show. Omit passwords, active message codes, complete financial information, and unrelated conversations. Ask what evidence is required, why it is needed, and through which secure channel it should be submitted. Keep the support case reference and any promised follow up, but do not invent a deadline that the operator has not stated. If multiple people respond, refer them to the same concise chronology so that instructions do not conflict. Good documentation cannot guarantee recovery, but it can reduce misunderstandings and show which question remains unresolved at each stage.
A recovery example with two possible endings
Meera tries to access an account after several months. Her saved password fails, and the supplied style of login page offers Forgot Password. Before selecting it, she checks the account identifier and the destination. She discovers that her saved entry belongs to a different host with similar branding. At this point the right action is to investigate the destination rather than reset a password through the unfamiliar page.
In another version of the situation, the destination and identifier are established, but the password record is genuinely obsolete. Meera enters the legitimate recovery route and reads its requests. If a message is sent to a channel she controls, she uses it only within the process she initiated. If the process instead depends on an old number, she pauses and asks the verified operator about ownership evidence. These endings illustrate why a recovery guide cannot honestly promise one universal sequence. The safe next action depends on the uncertainty actually present, and a process that is sensible in one case may be irrelevant in the other.
Keep the next access attempt simpler
After the issue is resolved, improve the private record that will support the next login. Record the account identifier, the destination you evaluated, the date of the credential change, and where the password is stored. Avoid retaining multiple unlabeled credentials that all appear current. A good record tells you what to use without exposing the secret to anyone reading a general account note.
If your contact details change later, review the operator's documented process before the old channel becomes unavailable. Do not assume that receiving messages at a new address means the account record has been updated. Where the interface offers a confirmation of a change, preserve the nonsecret result. If you decide not to continue using the account, investigate account closure through the operator's own terms rather than leaving the issue to a forgotten browser session. Recovery is an opportunity to make account management more understandable, whether the final decision is continued use, a pause, or a request to close the account.
Answers that should remain conditional
Does BDG Win password recovery require an OTP? The supplied reference does not answer that. Can support change a phone number? That process was not verified. Is a password reset guaranteed to restore a restricted account? No such promise is supported by the available evidence. Does an affiliate invitation code help recover ownership? Its presence in a registration link establishes no recovery authority or preference.
The practical questions are narrower and more useful: are you at the intended destination, are you identifying your own account accurately, do you understand what the current page requests, and can you keep each credential private? If the answer to any of those is uncertain, pause at that point. A careful recovery attempt can end with a restored account, a request for clarification, or a decision that the operator cannot currently provide enough information to continue. This article should support those decisions without inventing features, deadlines, or guarantees simply to make the process appear easier than the evidence allows.
Recovery should not require financial participation
Keep the access problem separate from any request to deposit money, purchase an upgrade, or participate in a game. The supplied login reference establishes no payment requirement for password recovery. If a person says payment is necessary to reveal a password or unlock the recovery process, ask for the identified operator's current written explanation and verify the recipient independently before taking any further step.
Do not treat a financial action as a diagnostic test. A payment cannot tell you whether you selected the right identifier or whether a suspicious recovery page belongs to the operator. It also creates a second issue if access remains unresolved afterward. Preserve the wording of the request and include it in a support question through a verified channel. If you cannot establish a legitimate basis for the request, stop. Recovering access should be understood through the account process that actually applies, not through an intermediary's unsupported promise that an additional transaction will make the problem disappear.